Skip to content
INTELLIGENCE BEAT2 Briefs

Privilege Escalation

2 Briefs

Verified technical decision briefs tracking privilege escalation developments

AWS patches untrusted search path flaw in OpenJD Sessions and Deadline Cloud worker
Topographic elevation contour card for AWS patches untrusted search path flaw in OpenJD Sessions and Deadline Cloud worker

What happened.Amazon Web Services released security updates fixing an untrusted search path vulnerability in the OpenJD Sessions runtime and AWS Deadline Cloud worker agent.

Why it matters.Cloud render farms process complex computational tasks across multi-user environments. When task runners load executable code from untrusted working directories, malicious users elevate privileges and access shared worker assets. Pipeline technical directors must update OpenJD Sessions and Deadline Cloud worker agents to the latest releases across all compute nodes.
Read Full Brief →
Source:AWS Security Bulletins (opens in a new tab)
All Stories1 story
Decision brief card for Microsoft patches critical Azure OpenAI missing authentication defect

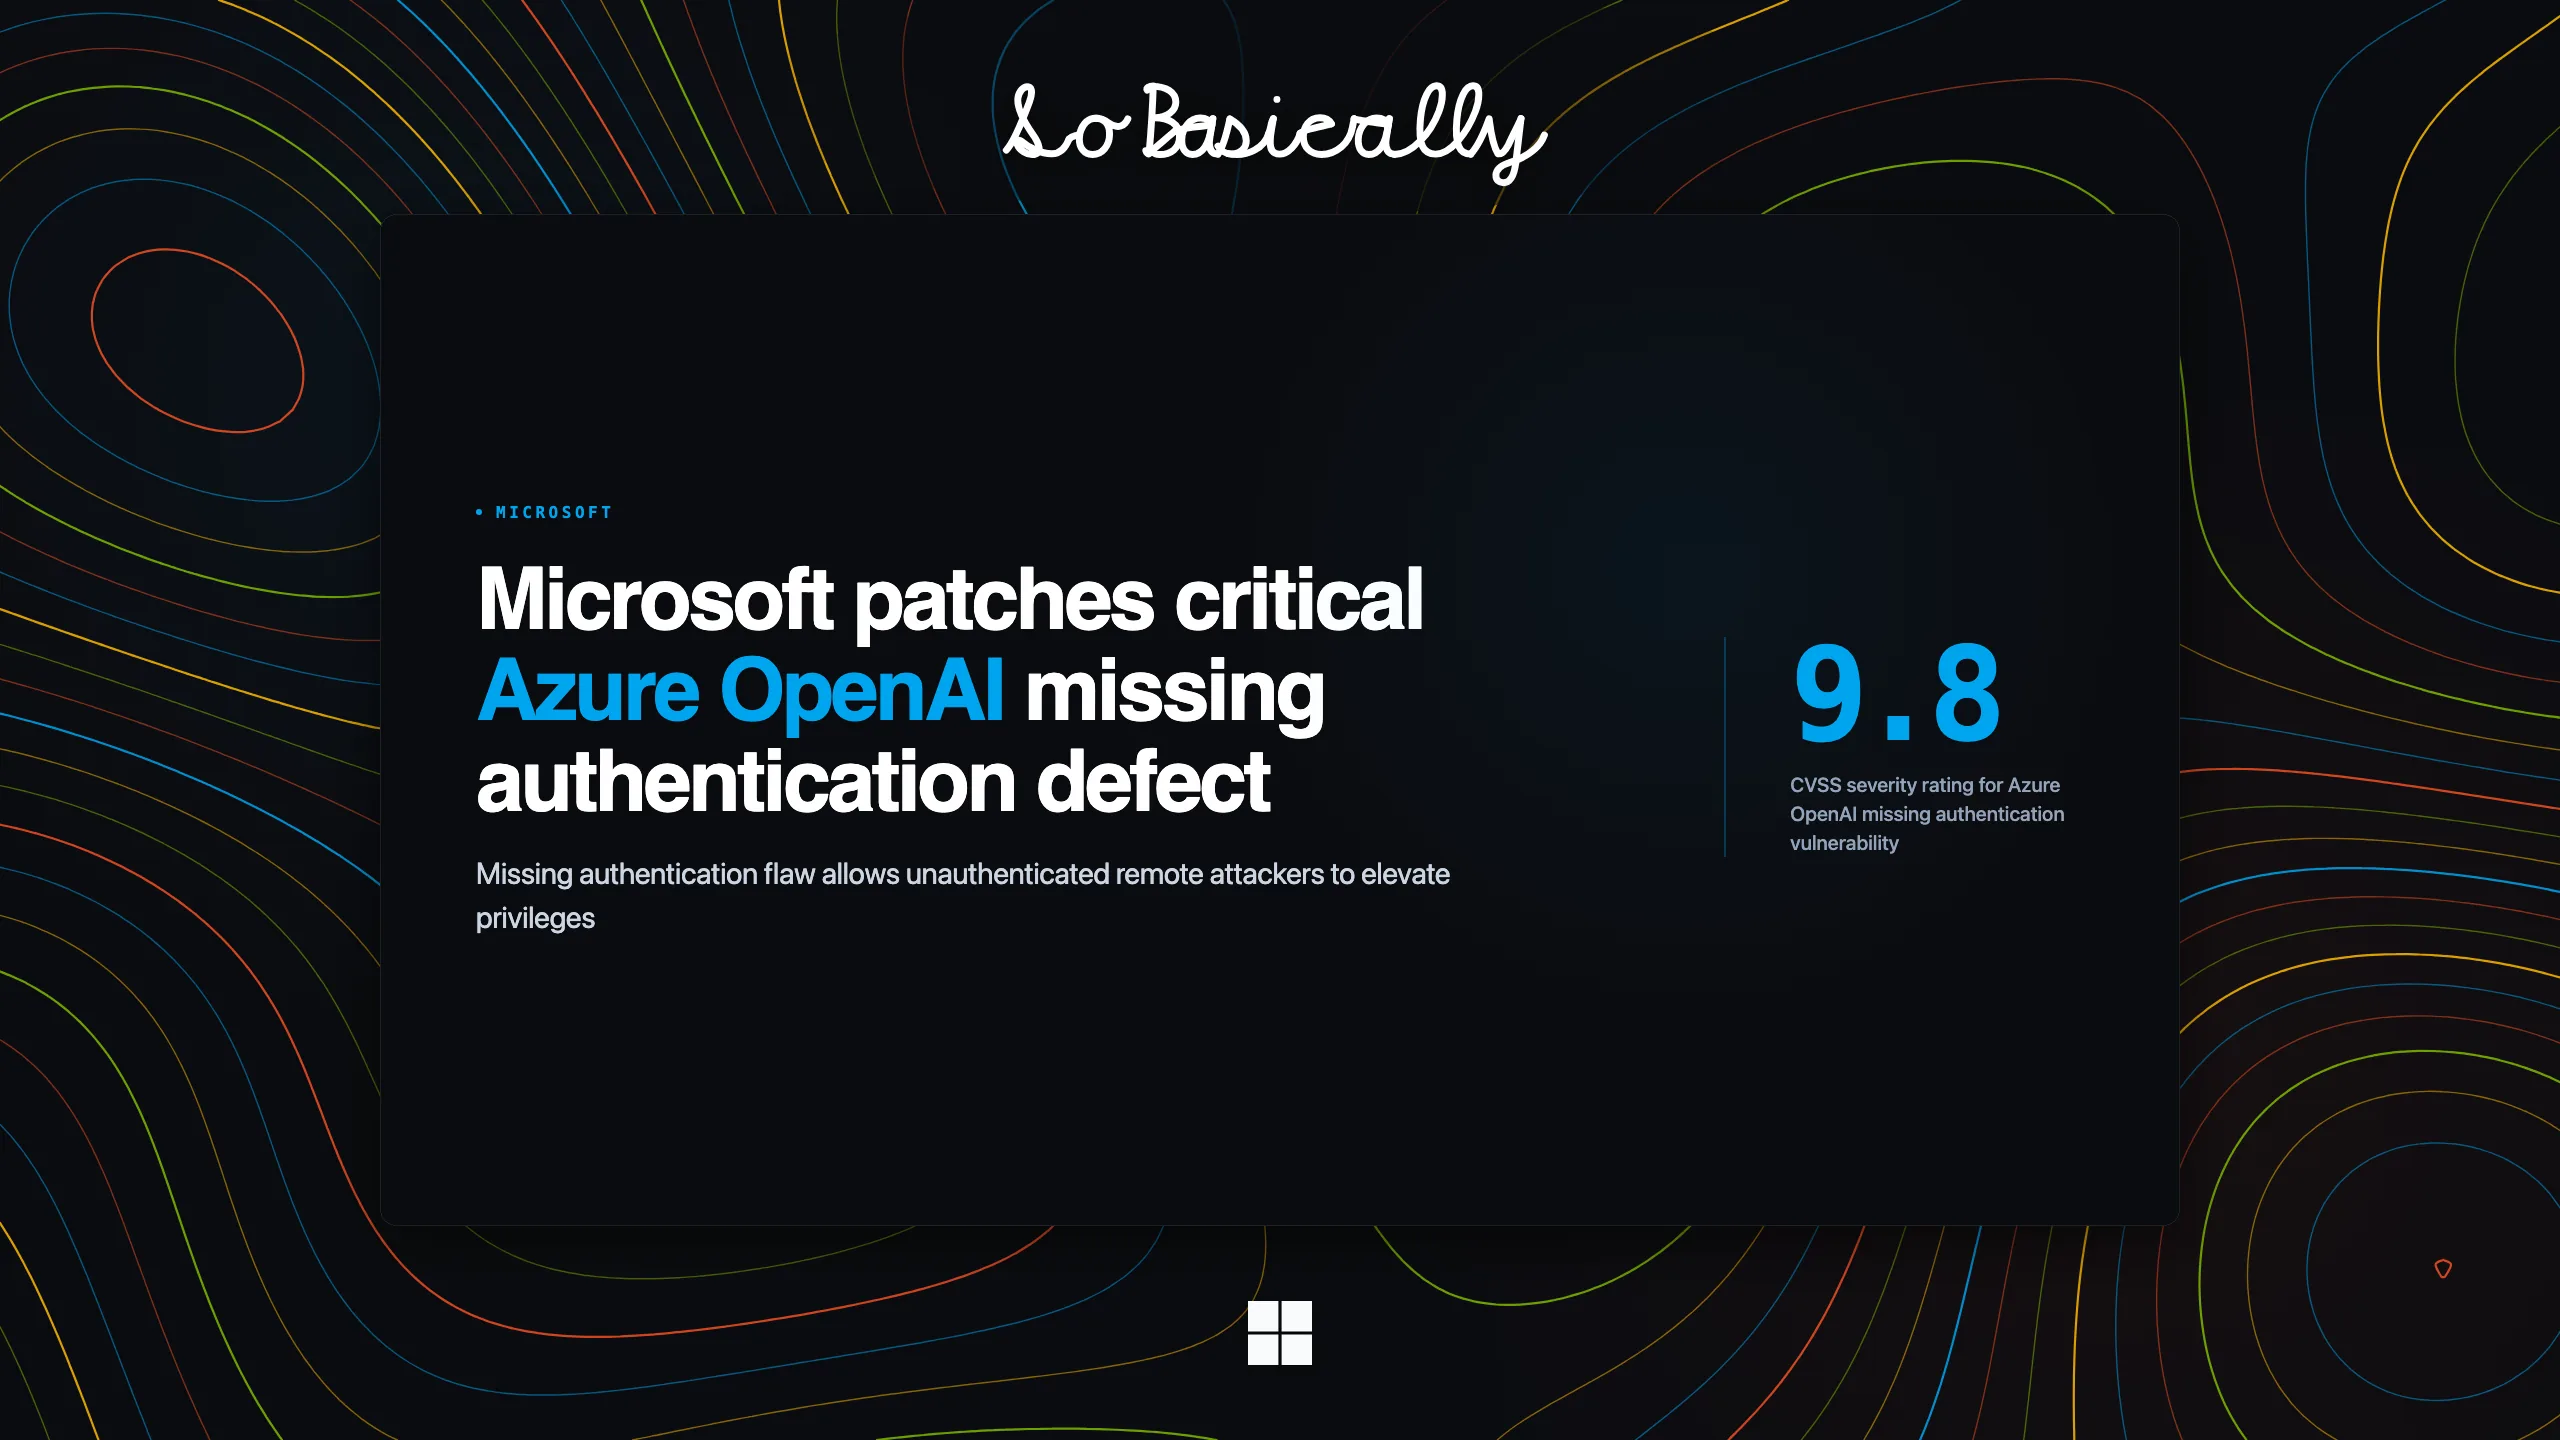
Microsoft patches critical Azure OpenAI missing authentication defect

What happened.Microsoft addressed a critical missing authentication flaw in Azure OpenAI during its November update cycle that allowed remote privilege escalation.

Why it matters.Enterprise teams integrate Azure OpenAI endpoints to deploy private language models and process proprietary corporate documents. When missing authentication vulnerabilities expose model infrastructure, attackers access private machine learning models and manipulate enterprise artificial intelligence workloads. Cloud security architects should review API management firewall rules and restrict model endpoint access to private virtual networks.

  • Vulnerability mechanics: Tracked as CVE-2026-119990 with a 9.8 CVSS score, the defect stems from missing authentication checks on critical operational endpoints.
  • Exploitation path: Unauthenticated remote attackers send crafted network payloads directly to model serving interfaces without providing API credentials.
  • Administrative impact: Successful exploitation allows network actors to bypass tenant authentication boundaries and execute privileged administrative functions.
  • Related disclosures: The monthly release also fixed CVE-2026-119958, a 9.8 CVSS remote code execution vulnerability in the Windows LDAP service.
  • Remediation release: Microsoft deployed automated infrastructure updates across Azure OpenAI cloud regions, requiring zero administrative endpoint interventions.
Official Source:Microsoft Security Response Center
Decision brief card for Microsoft patches critical Azure OpenAI missing authentication defect
↳Continues: Microsoft patches actively exploited zero-day Outlook NTLM hash theft vulnerability
Read Brief
Source:Microsoft Security Response Center (opens in a new tab)