Node.js patches critical Brotli decoder buffer overflow vulnerability
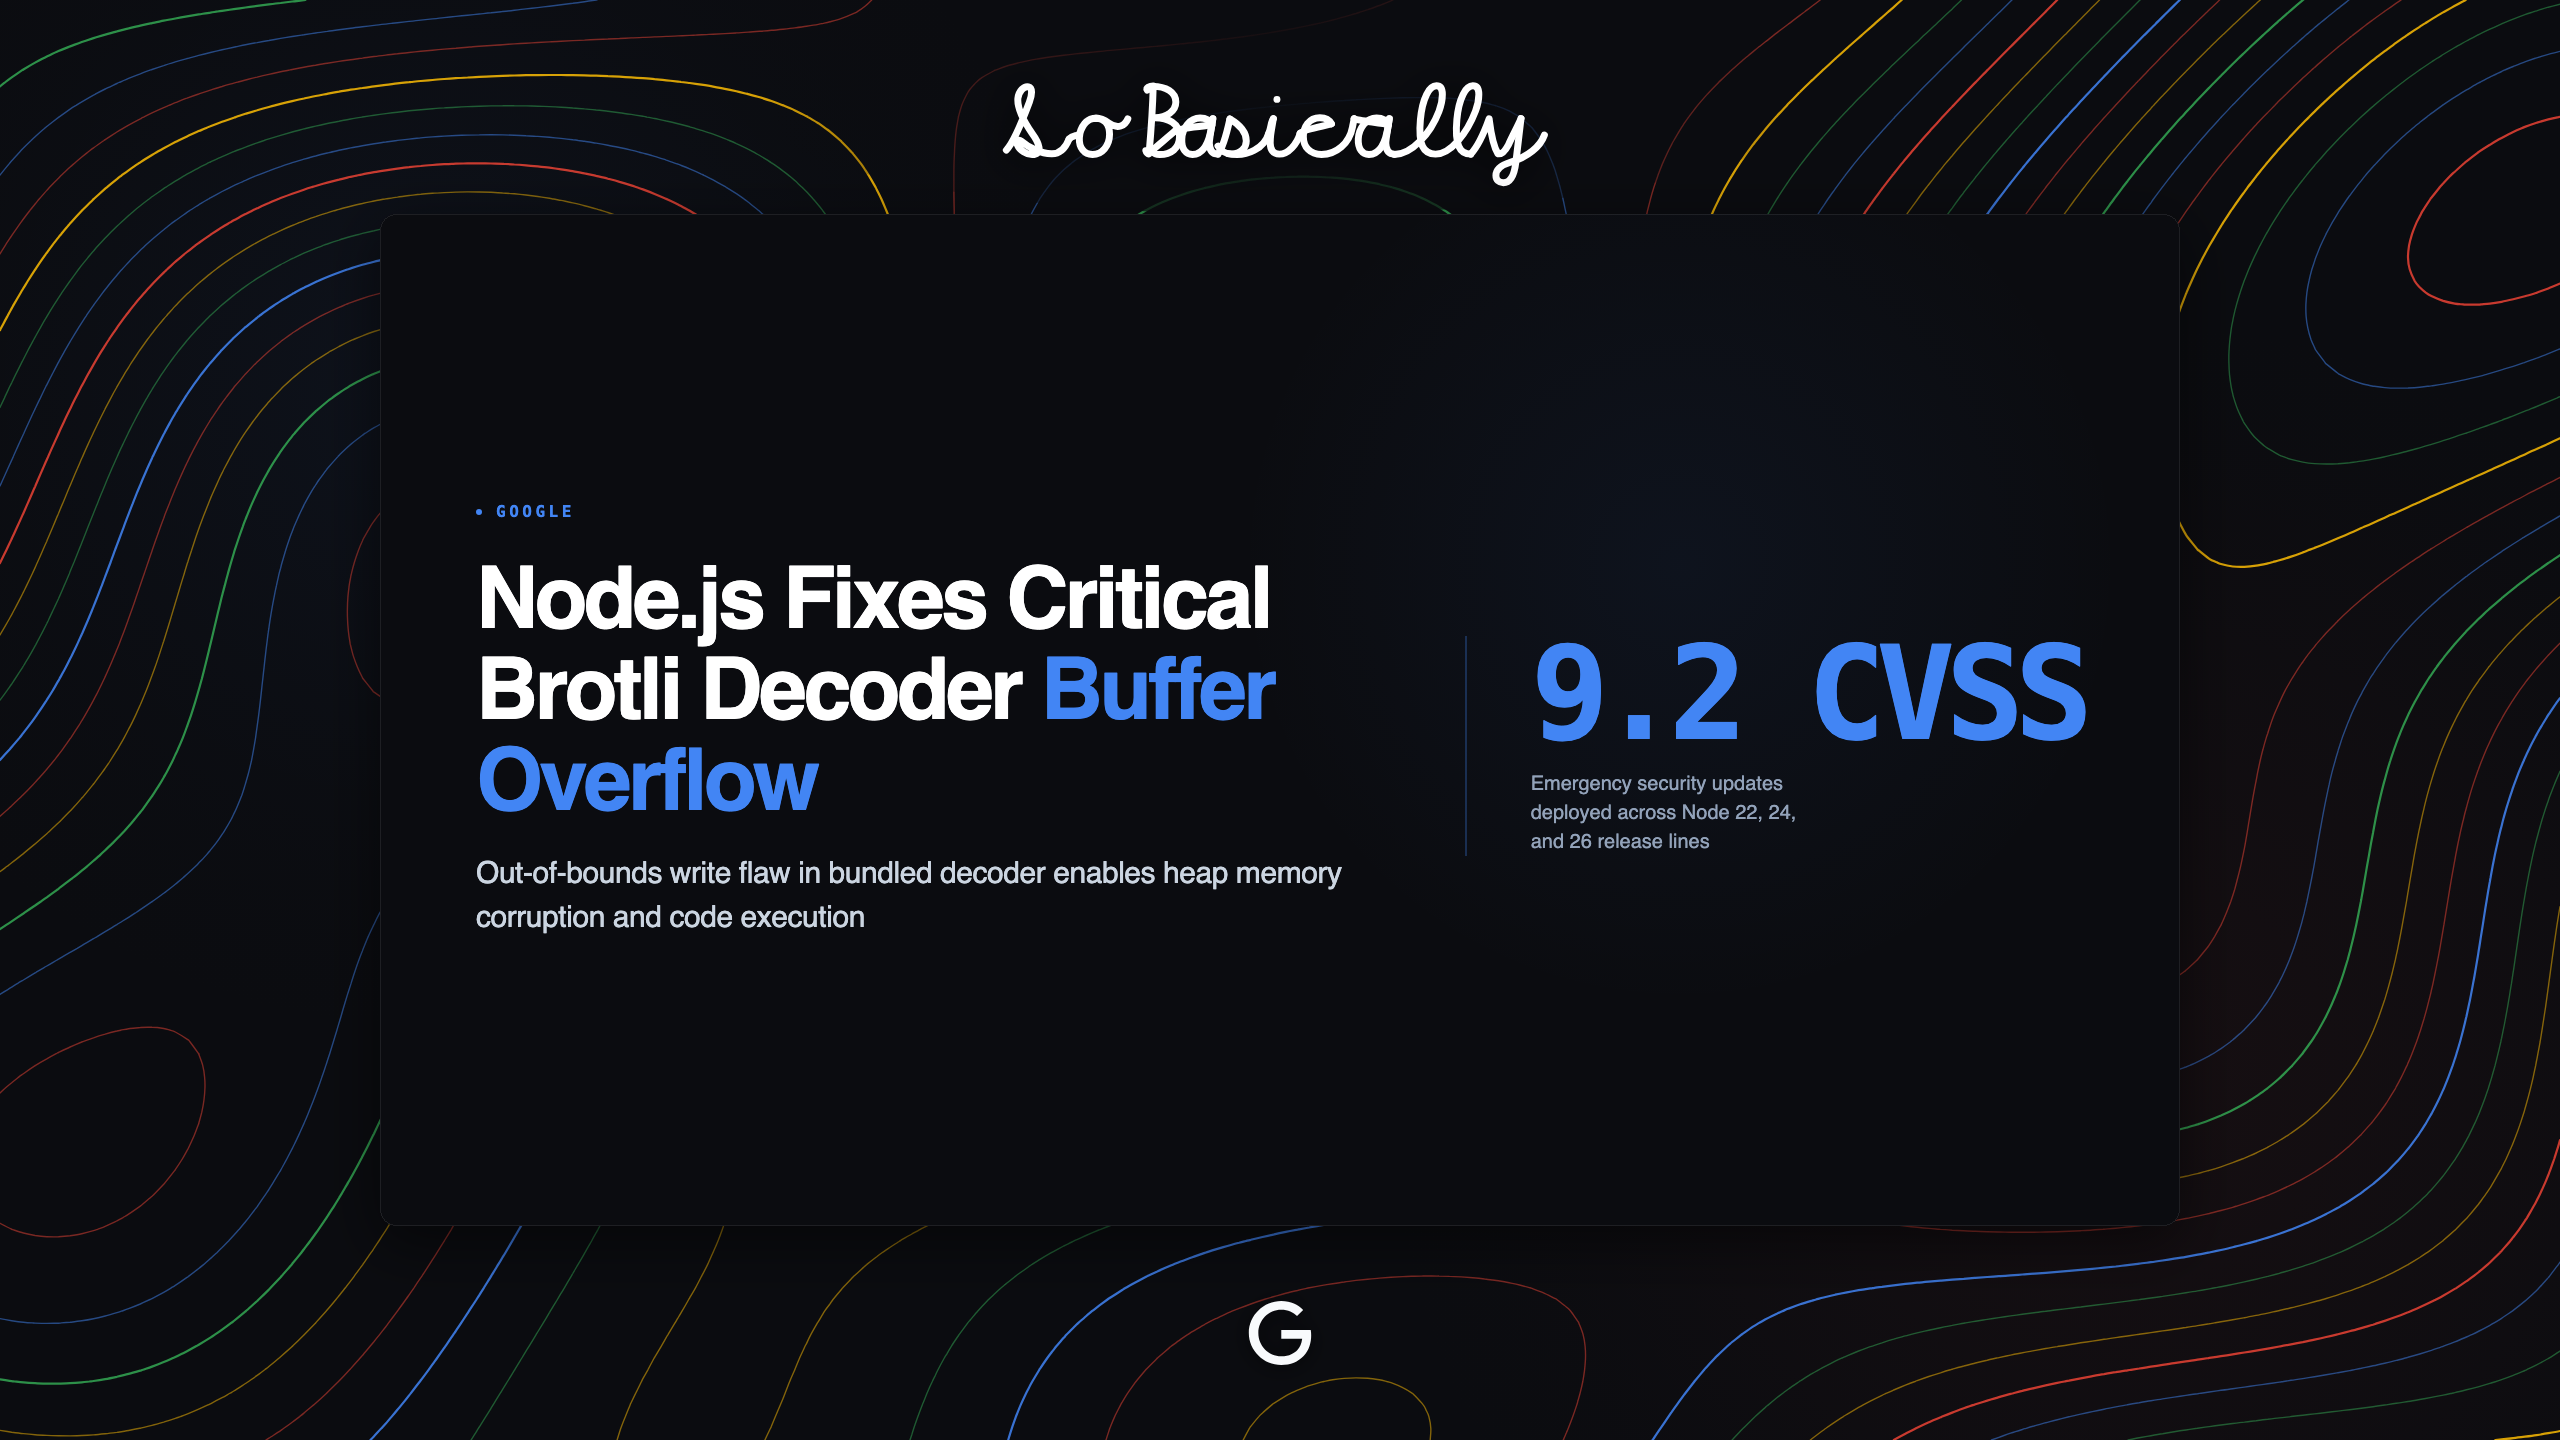
What happened.The Node.js project published emergency security updates across all active release lines to patch a critical out-of-bounds write buffer overflow vulnerability within the bundled Google Brotli compression decoder.
Why it matters.Node.js powers microservice edge gateways, API routers, and server-side rendering pipelines that routinely decompress untrusted user requests. Infrastructure teams must update Node container runtimes and backend worker images to patched releases before public exploit scripts proliferate.