 CiscoAnalysis
Cisco warns of active ASA and FTD SSL VPN denial of service attacks
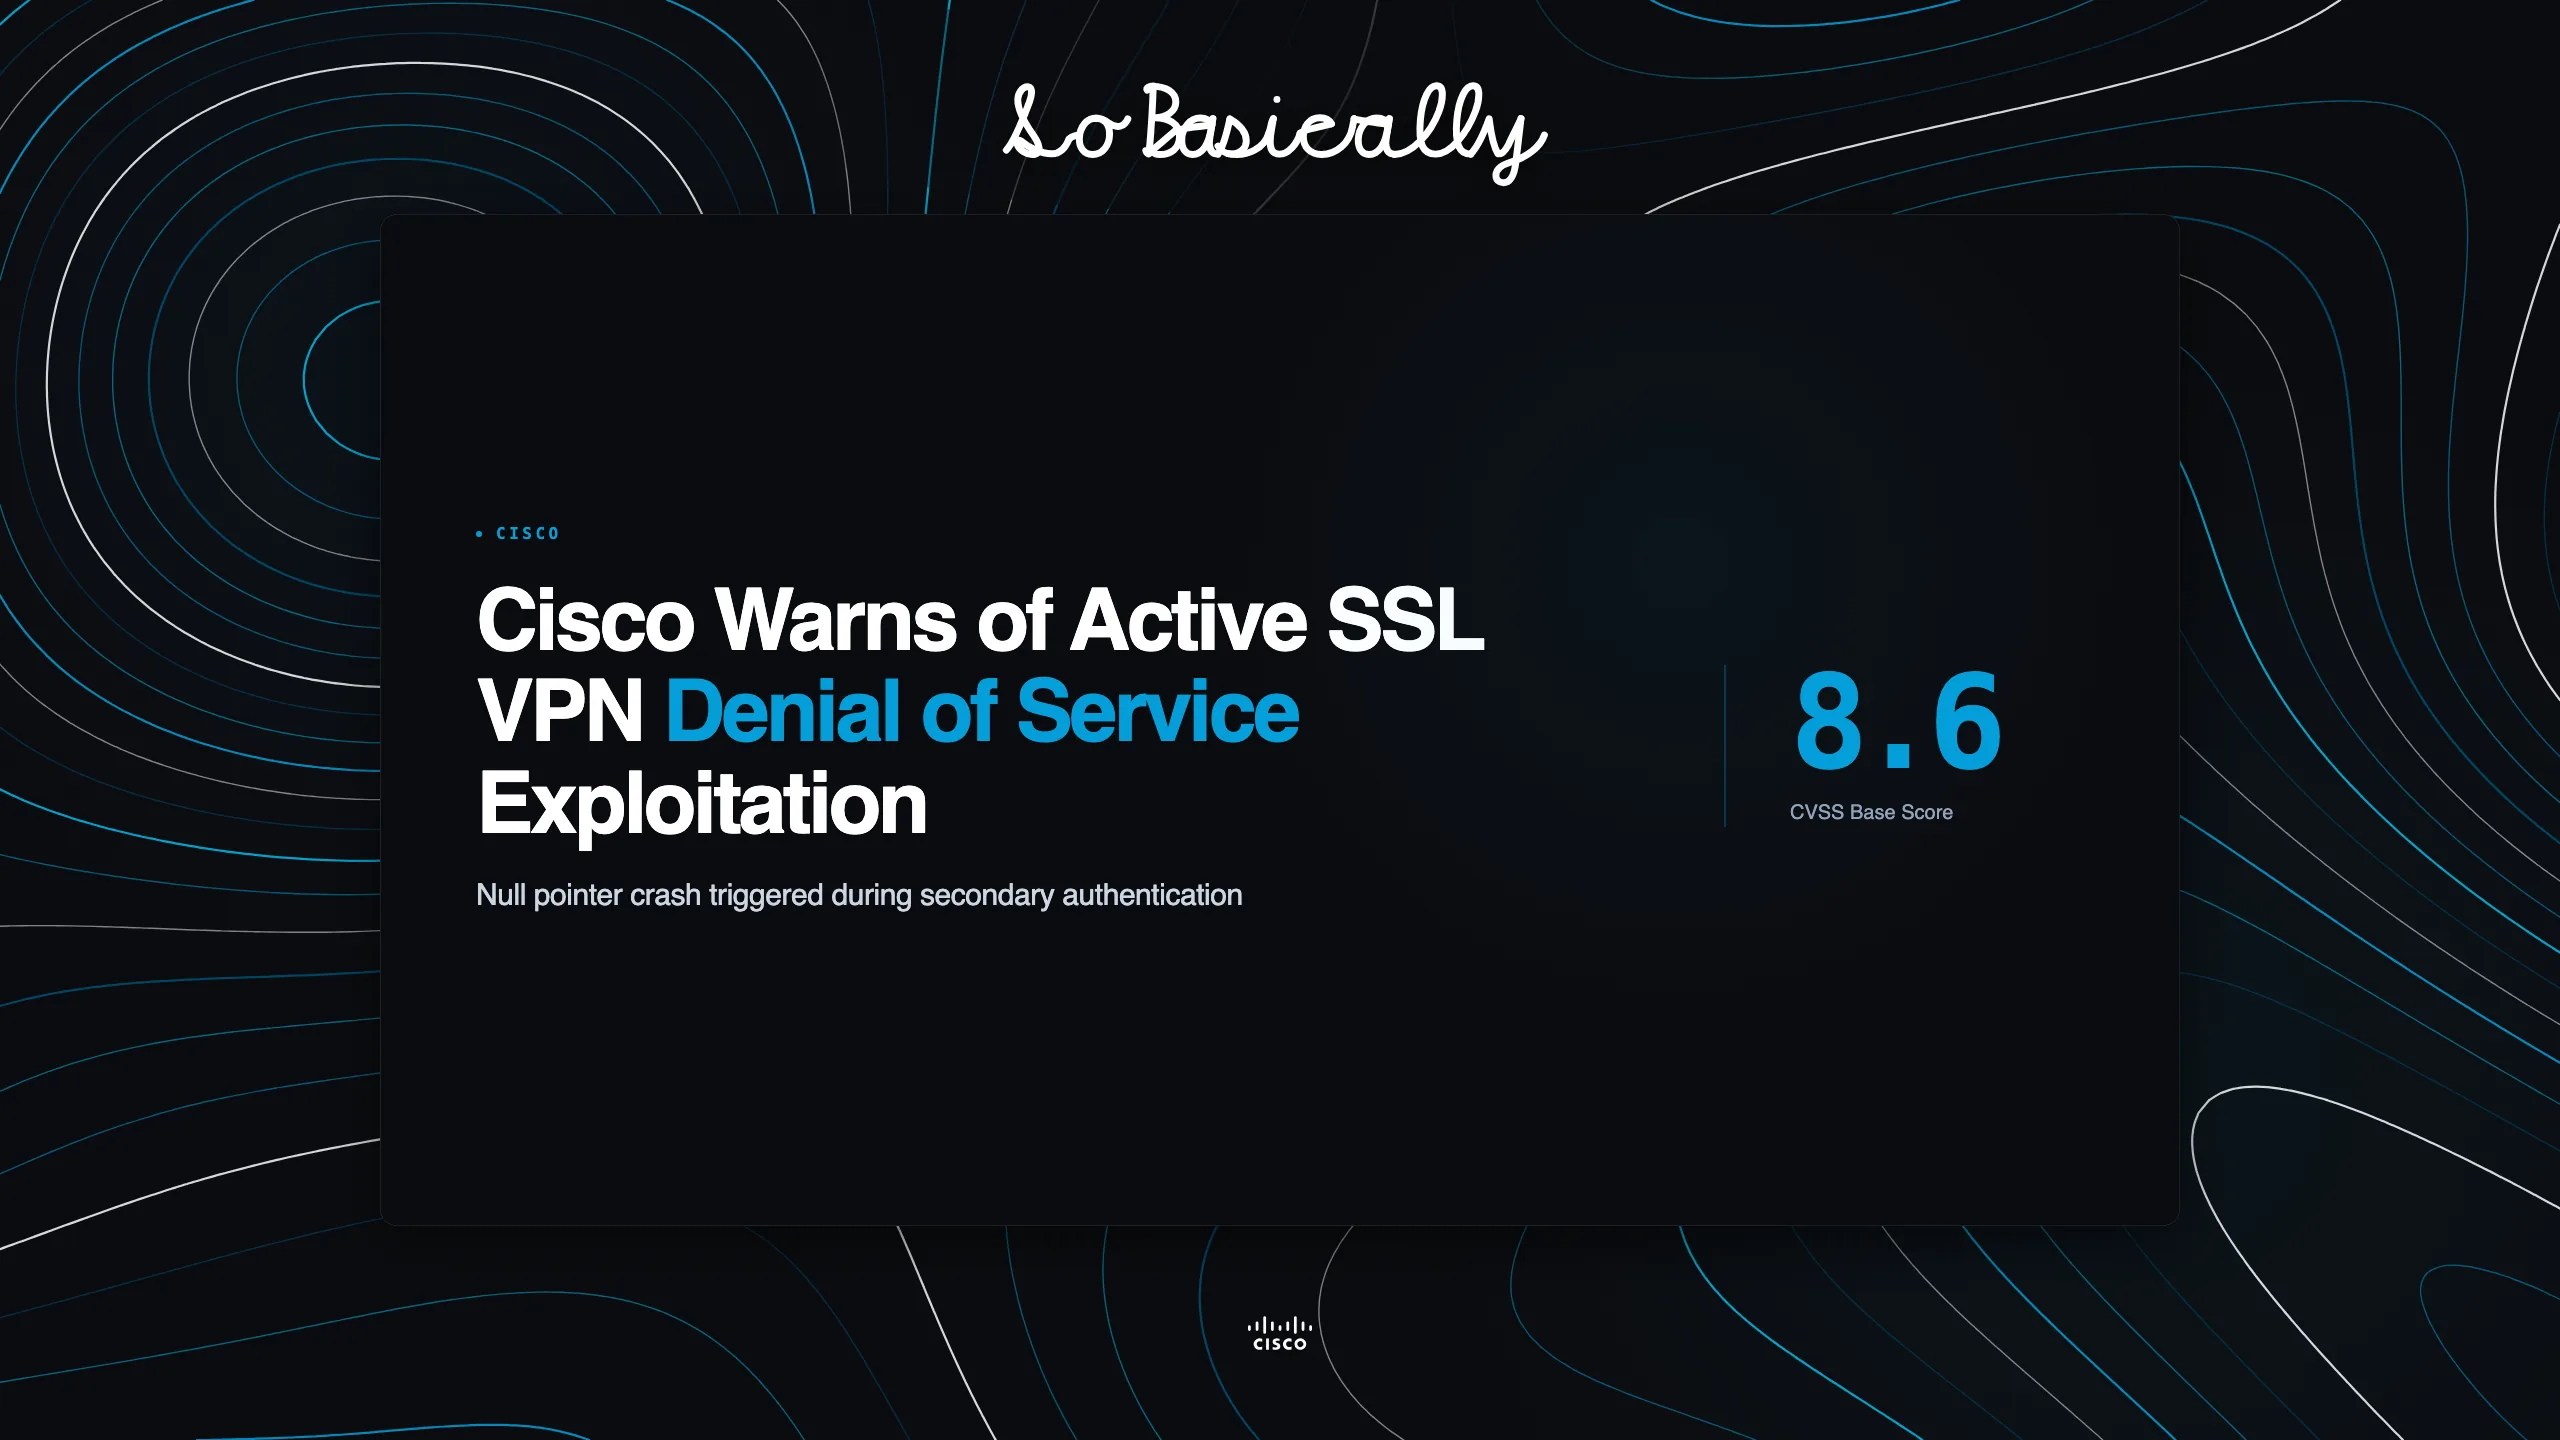
What happened.Cisco published a high-severity security advisory warning that threat actors are actively targeting an unauthenticated denial of service vulnerability affecting Secure Firewall ASA and Threat Defense software.
Why it matters.Perimeter security appliances provide secure remote connectivity for distributed corporate workforces. When remote attackers can trigger continuous device reloads through unauthenticated network probes, entire corporate VPN infrastructures face sustained outages. Network engineering teams must verify whether secondary authentication is enabled on external tunnel groups and apply fixed firmware images. Security operations centers should monitor perimeter firewall logs for repeated unexpected reload events.
The technical specifications:
- Vulnerability mechanics: Tracked as CVE-2026-76418 with an 8.6 CVSS score, a logic error in error handling occurs when secondary authentication is enabled on remote access SSL VPN tunnel groups.
- Exploitation path: Unauthenticated remote attackers transmit crafted connection packets to exposed SSL VPN endpoints, triggering null pointer dereferences that force affected gateway devices to crash and reload unexpectedly.
- Remediation releases: Cisco released software updates across affected ASA and FTD release trains, advising network administrators with active secondary authentication configurations to upgrade immediately.
STORYLINE PROGRESSION & CONTEXT
This report represents a verified evolution of prior newsroom intelligence: