 CISAAnalysis
CISA adds Linux kernel Fragnesia and VMware ESX flaws to KEV catalog
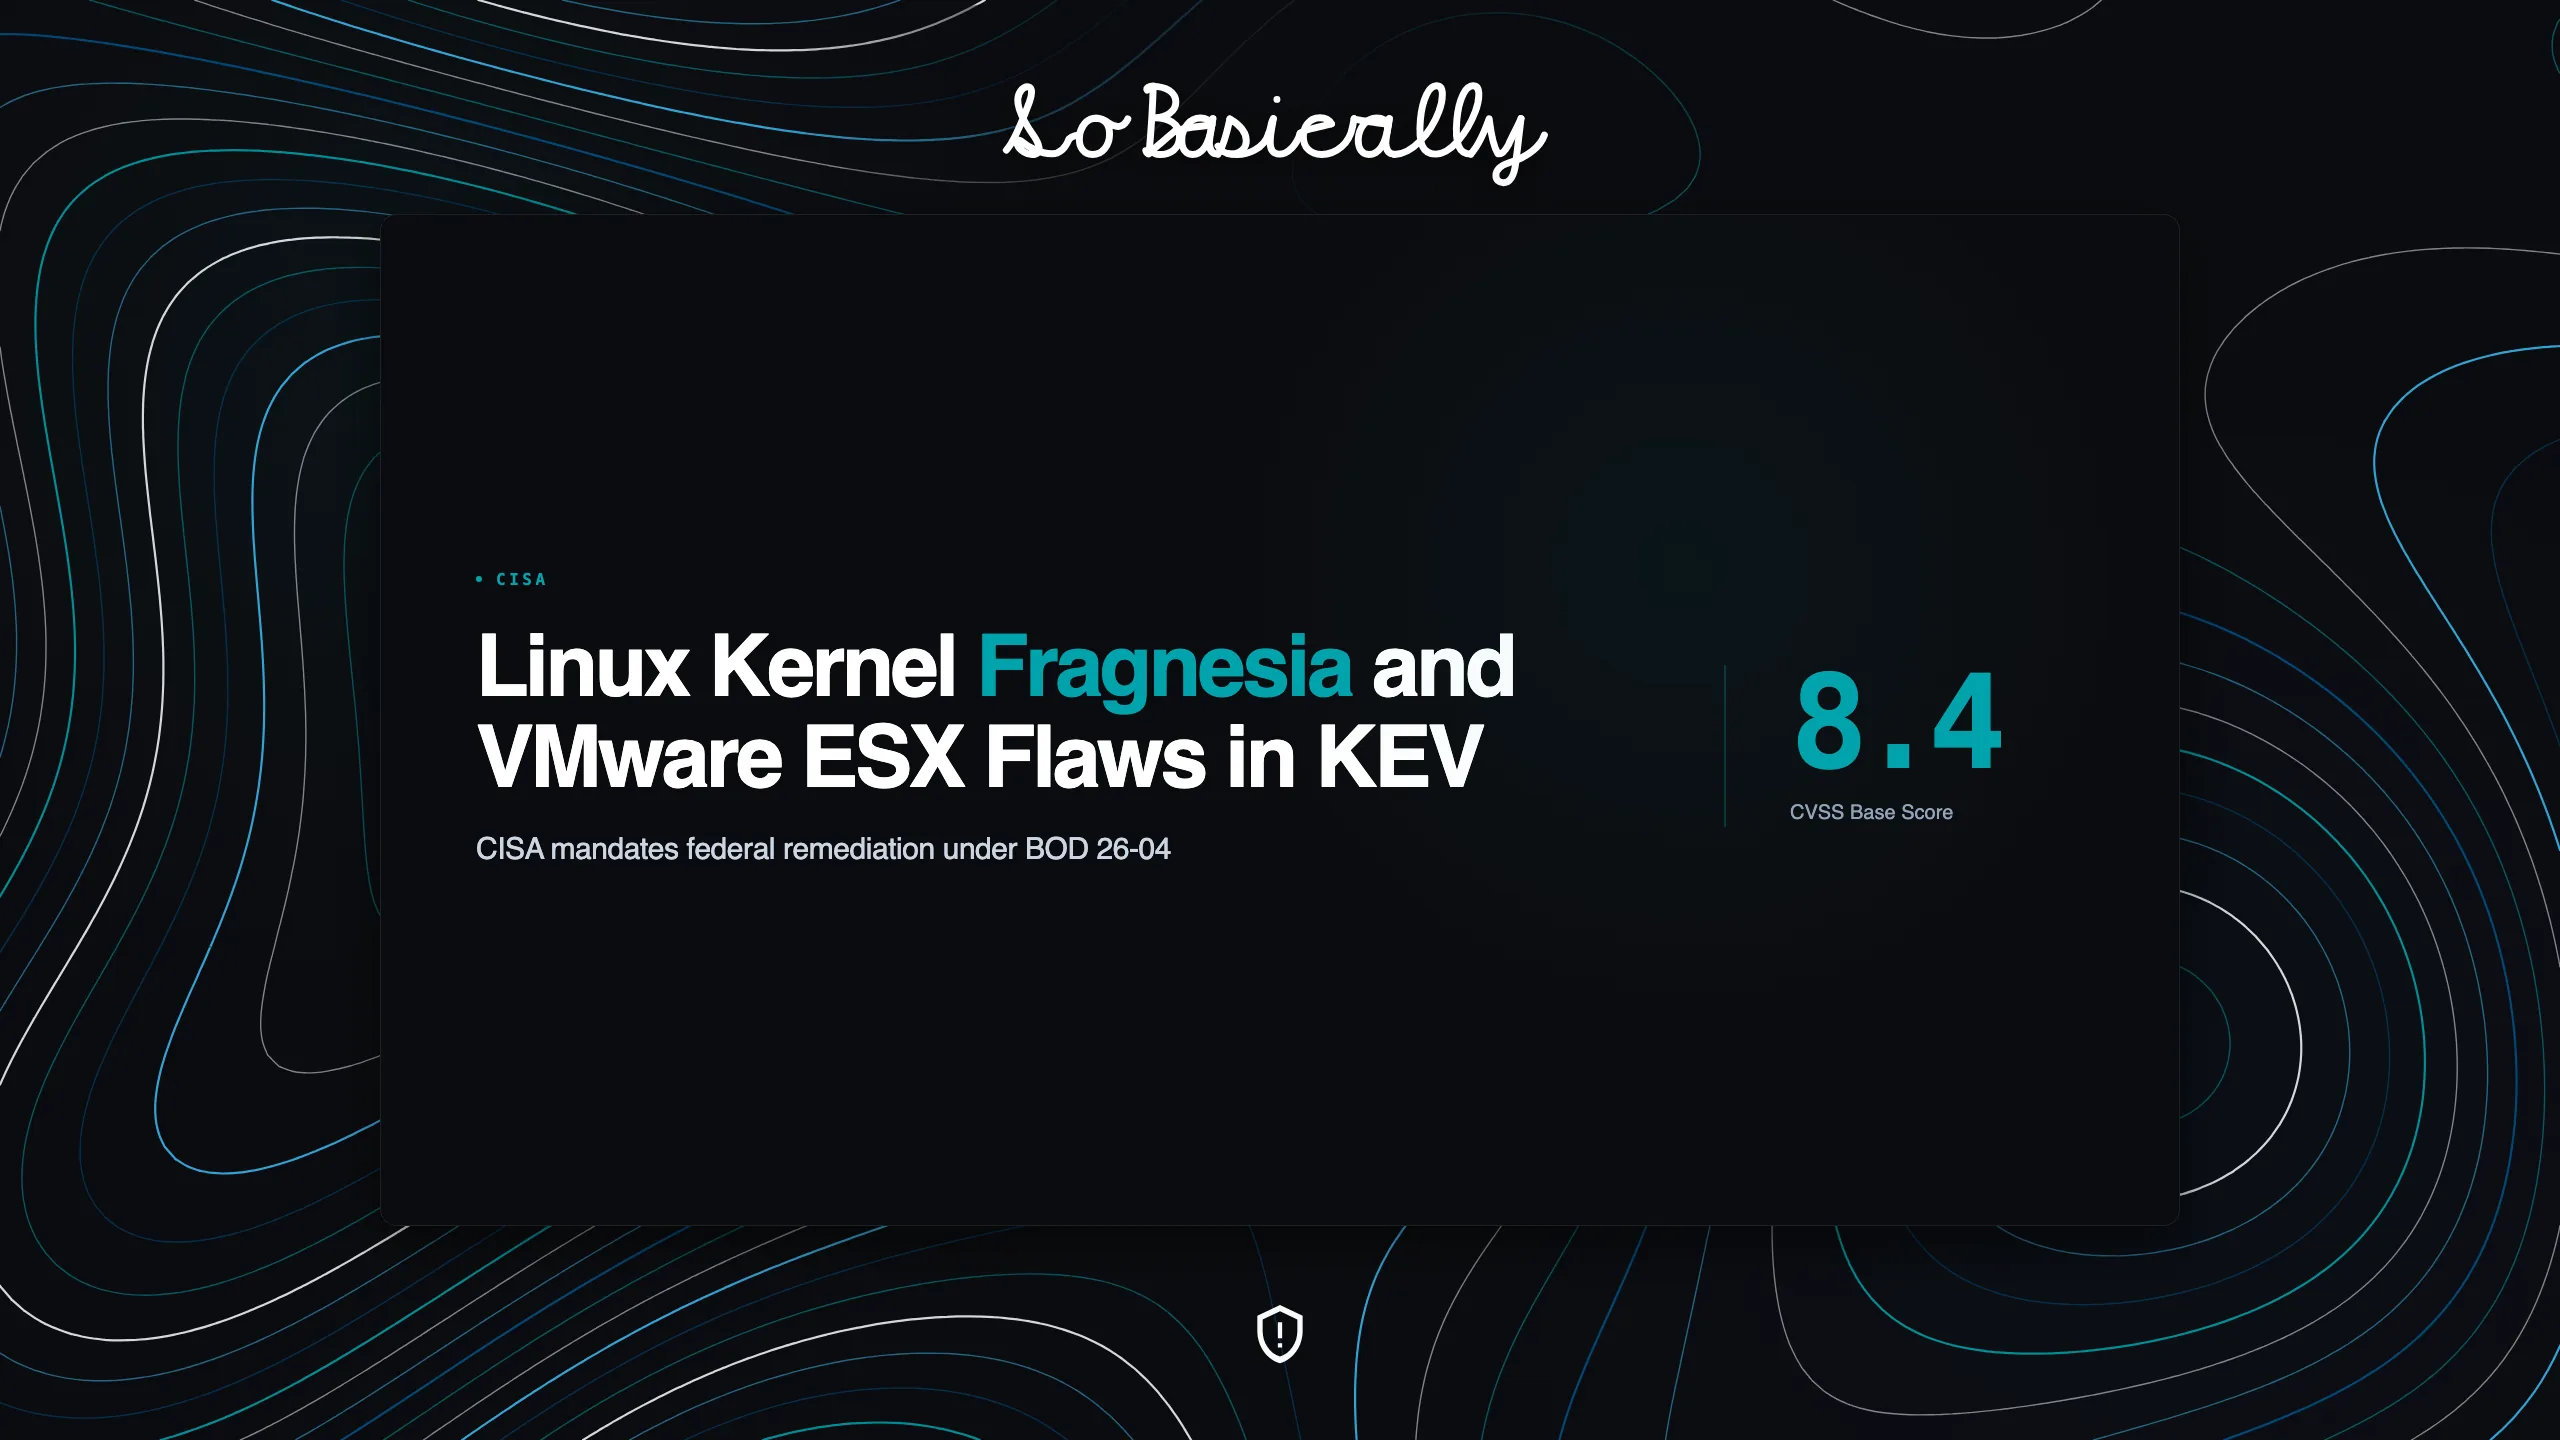
What happened.CISA added the Linux kernel Fragnesia privilege escalation flaw and a VMware ESX logging defect to its Known Exploited Vulnerabilities catalog following active in-the-wild exploitation.
Why it matters.Container environments and service sandboxes rely entirely on kernel memory boundaries. When network socket handling allows unprivileged processes to alter file-backed memory caches directly, local access controls fail completely. Systems administrators must upgrade host kernels and virtualized infrastructure nodes immediately. Engineering teams should audit system logs for unauthorized TCP encapsulation activity.
The technical specifications:
- Vulnerability mechanics: Tracked as CVE-2026-46300 with an 8.4 CVSS rating, Fragnesia exploits improper socket buffer coalescing to allow deterministic writes to the page cache of read-only files.
- Exploitation path: Adversaries chain Fragnesia with web runtime exploits to escape process sandboxes, modify cached setuid binaries in memory, and acquire root access across Linux hosts.
- Remediation releases: CISA issued Binding Operational Directive 26-04 mandating federal agencies remediate affected Linux kernels and VMware ESX hypervisors by October 31, 2026, while conducting forensic triage for compromise indicators.
STORYLINE PROGRESSION & CONTEXT
This report represents a verified evolution of prior newsroom intelligence: