SonicWall patches critical pre-authentication SSRF in SMA 1000 appliances
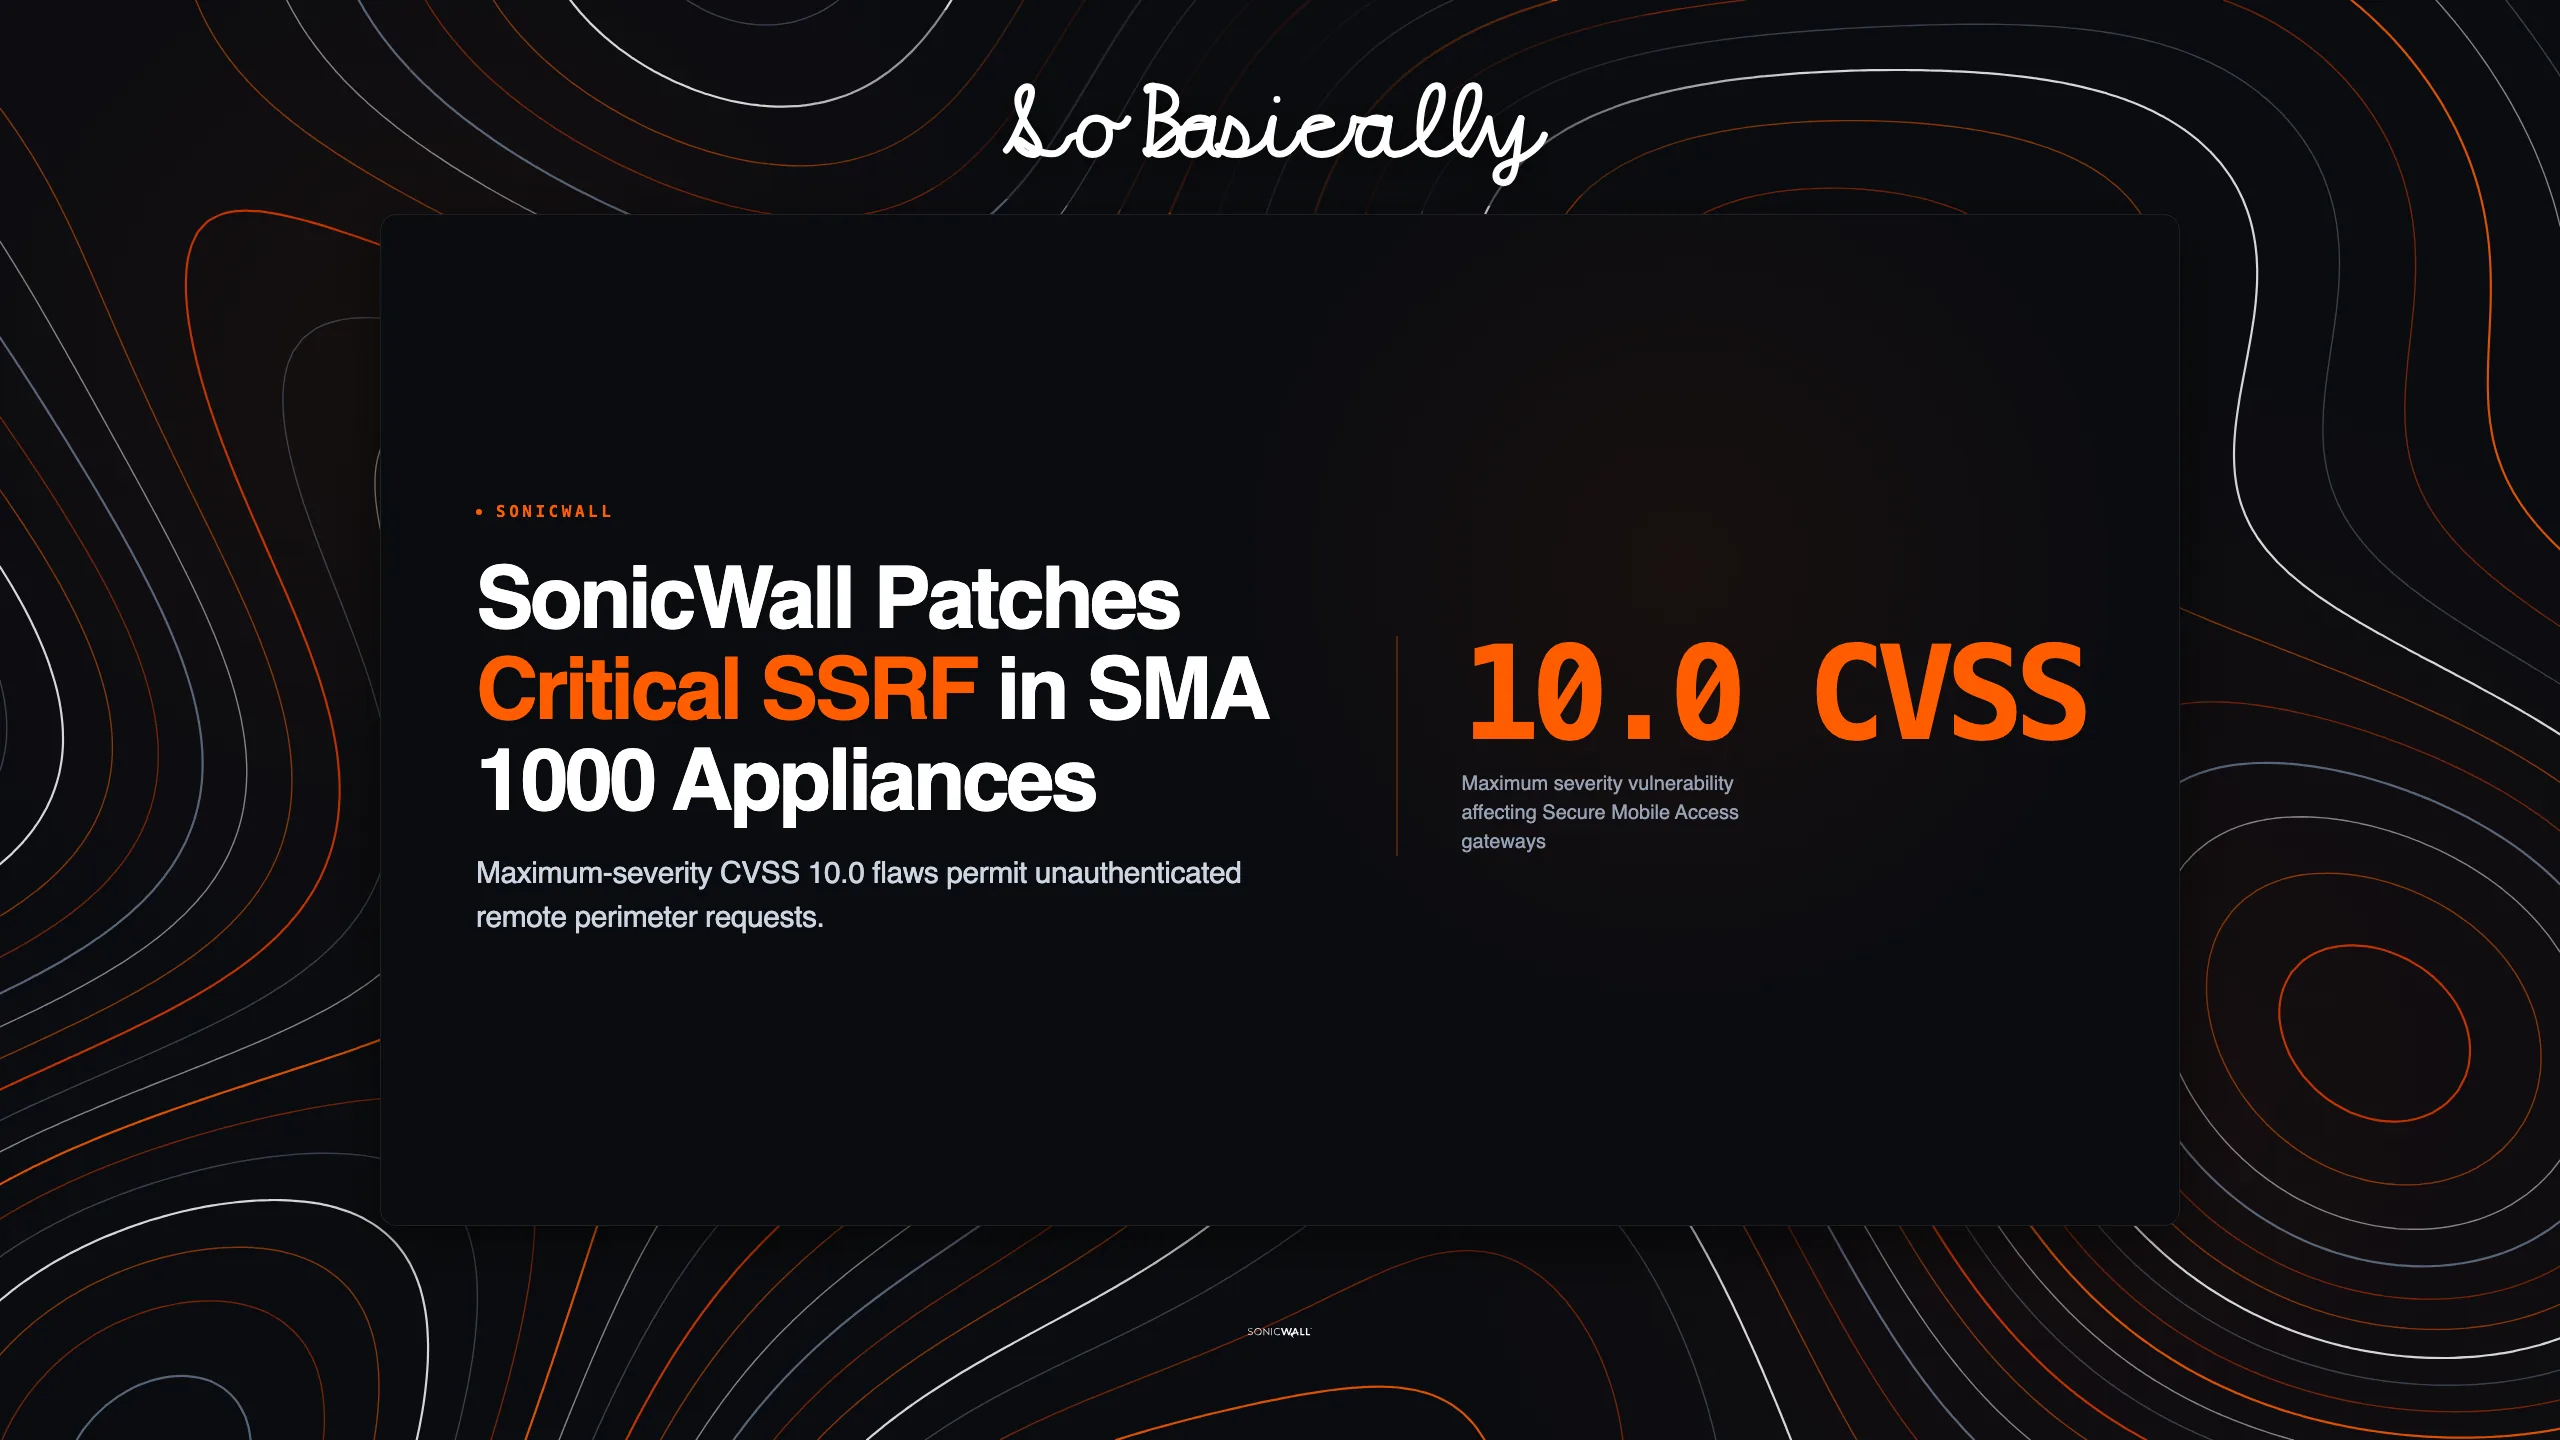
What happened.SonicWall published security advisory SNWLID-2026-0017 addressing a maximum-severity pre-authentication server-side request forgery flaw and a command injection defect across its Secure Mobile Access 1000 series appliances.
Why it matters.Enterprise remote access appliances serve as the frontline perimeter gateway for remote corporate workforces. When unauthenticated actors exploit request forgery flaws on public-facing gateways, internal network segmentation boundaries collapse without administrative authentication. Infrastructure engineering teams must apply SonicWall platform hotfixes immediately across all physical and virtual gateways. Security architects should restrict administrative access interfaces strictly to isolated management subnets.