Skip to content
SoBasicallyVOL. I · RUN 2026-10-25-cybersecurity-advisories
ARCHIVAL EDITION2026-10-25-cybersecurity-advisories4 STORIES · 562 WORDS
← Back to Archive

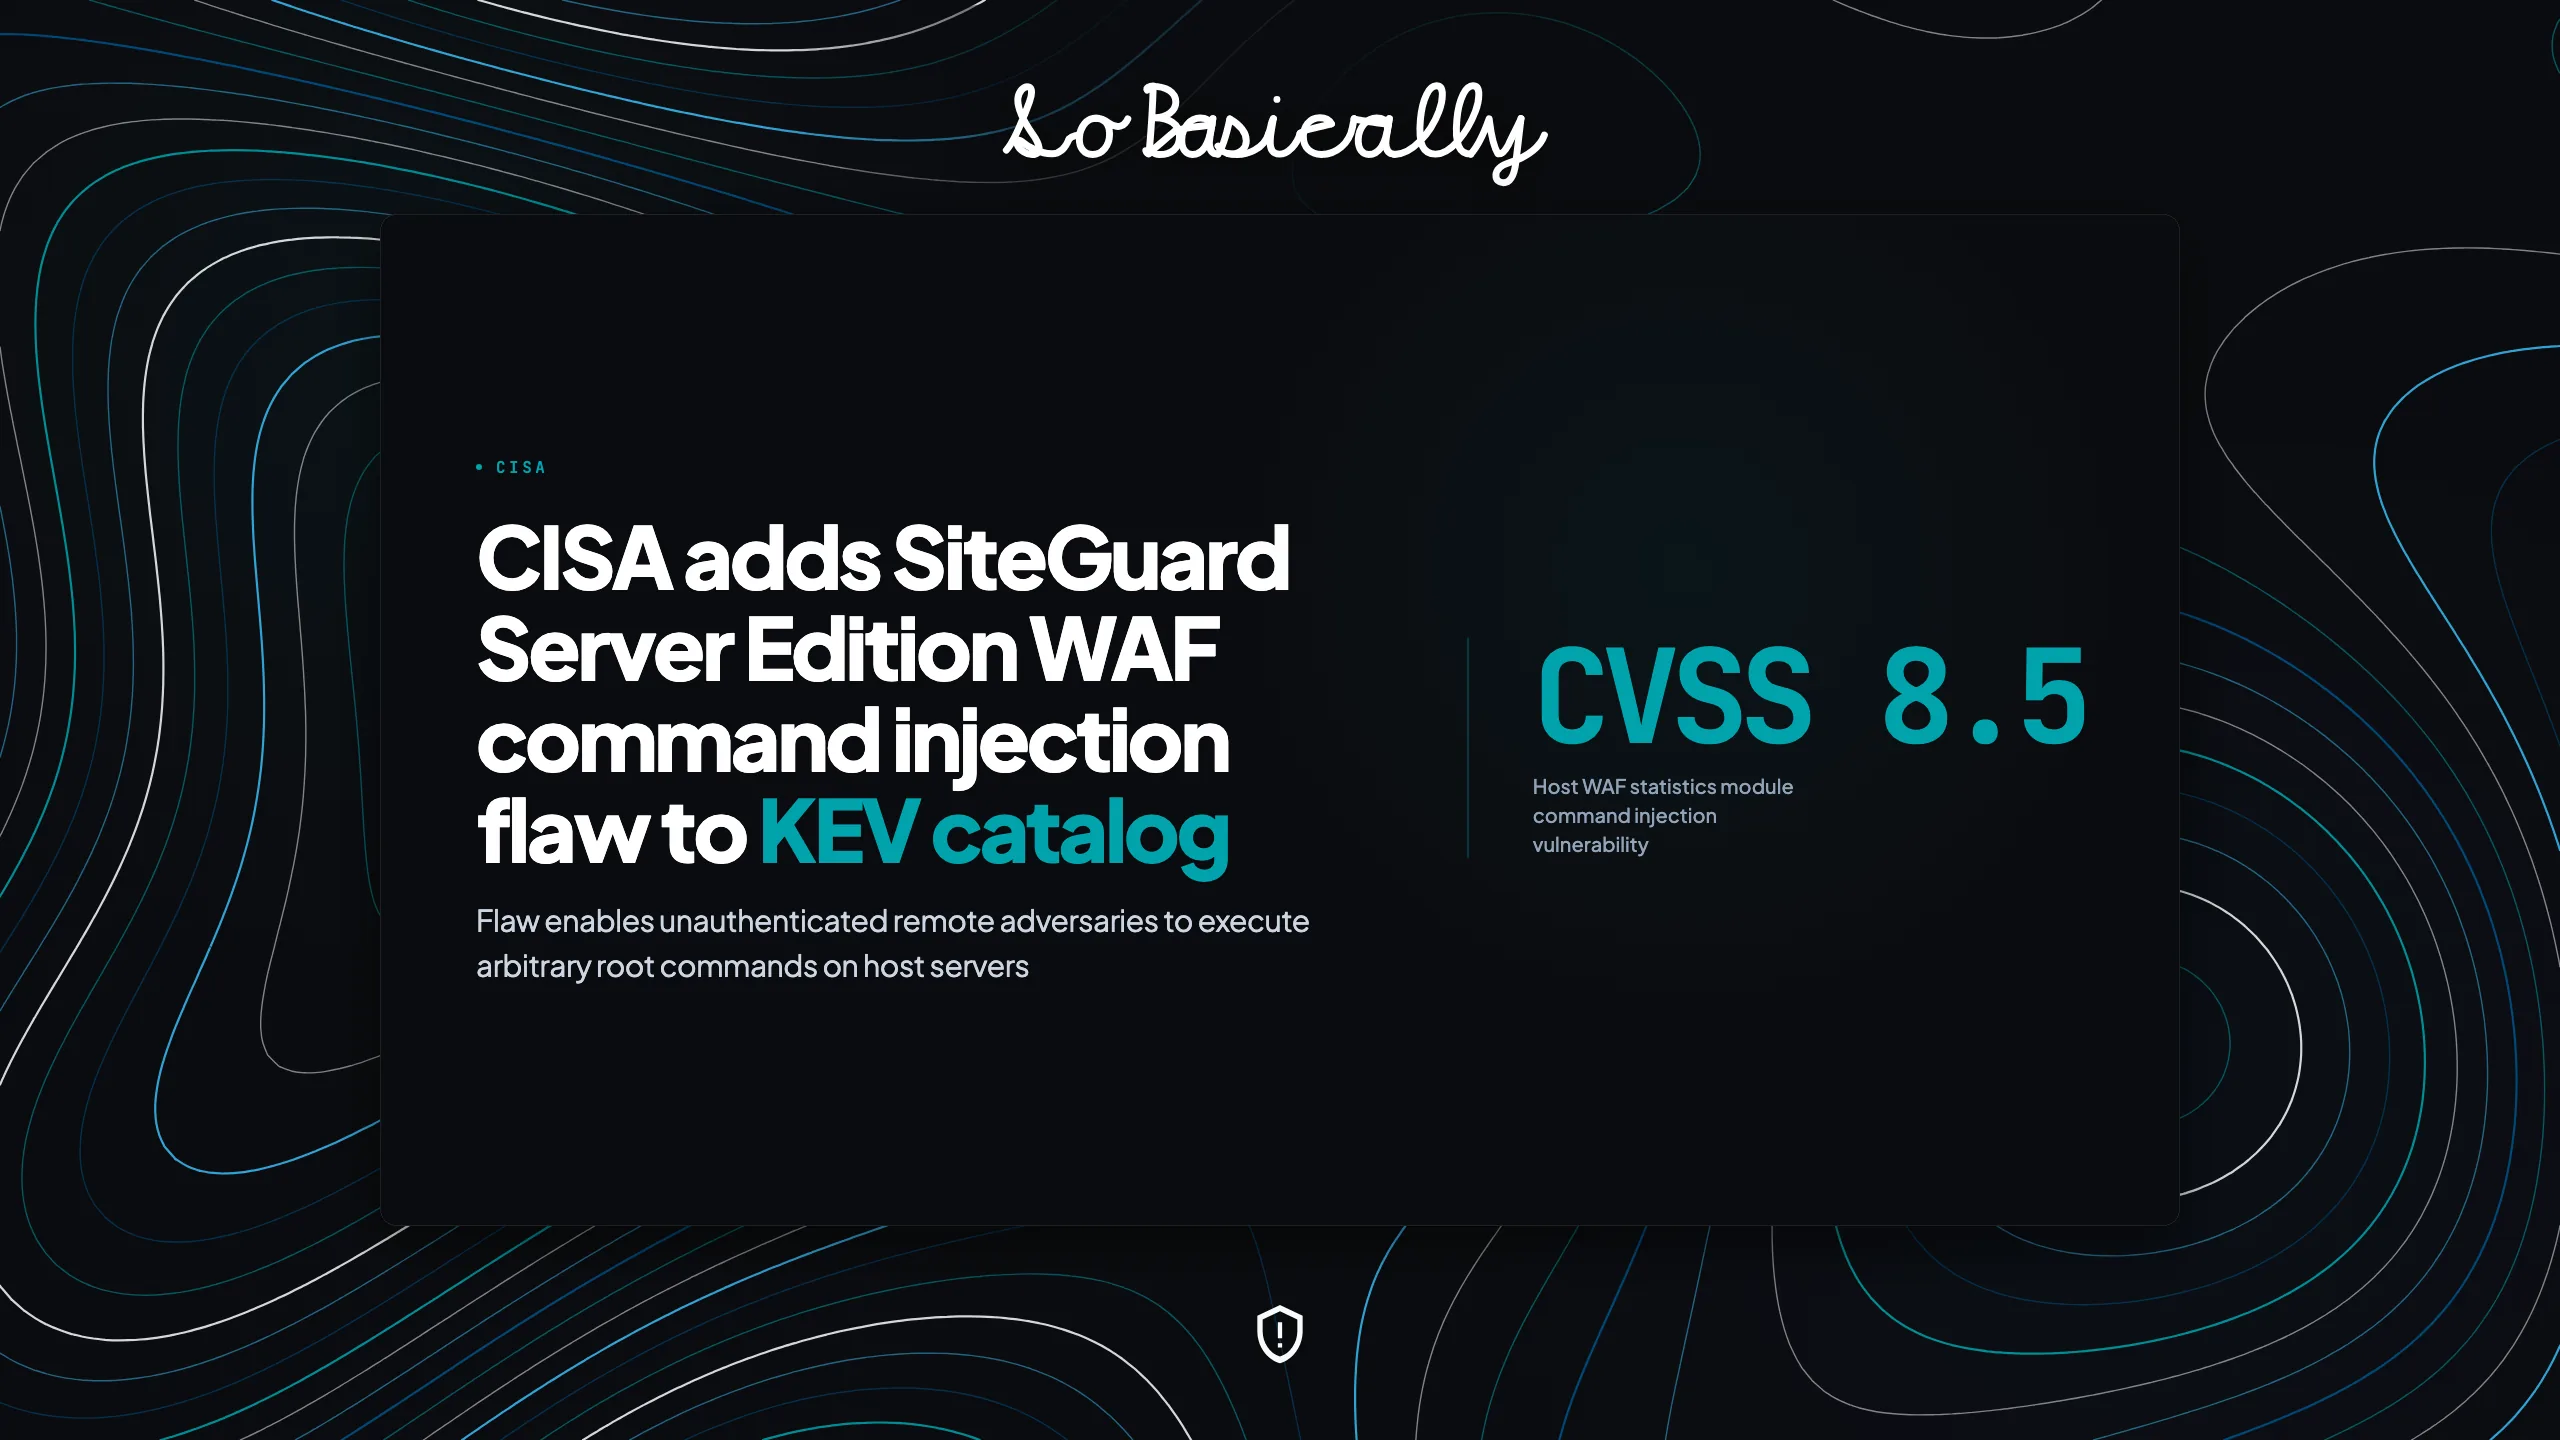
CISA adds SiteGuard Server Edition WAF command injection flaw to KEV catalog
Topographic elevation contour card for CISA adds SiteGuard Server Edition WAF command injection flaw to KEV catalog

What happened.CISA added an actively exploited OS command injection defect in EG Secure Solutions SiteGuard Server Edition to its Known Exploited Vulnerabilities catalog.

Why it matters.Host-based web application firewalls run directly alongside web servers to inspect incoming traffic and enforce filtering policies. A compromised host firewall turns a security perimeter into an adversary stronghold with kernel and system privileges. Teams operating Apache, Nginx, or IIS servers with SiteGuard must apply vendor maintenance builds and inspect process logs for unauthorized shells.

↳Continues storyline: CISA adds Collabora Online CODE server command injection flaw to KEV catalog
Read Full Brief →
Source:NIST NVD (opens in a new tab)
VERIFIED STORIES IN THIS EDITION3 STORIES
CANDIDATE INTELLIGENCE · UNVERIFIED LEADS

The Discovery Wire · Unverified Attention Signals

Candidate storylines identified across developer channels. Under newsroom canon, attention never establishes fact; these leads remain quarantined until supported by Tier 1 official records.

DEVELOPER WIRE

Oracle Java SE and GraalVM JSSE intermediate CA trust bypass (CVE-2026-91403)

Critical CVSS 9.1 remote trust bypass vulnerability in JSSE enabling unauthenticated certificate forgery via weak intermediate CA keys. Held on watchlist pending downstream distribution updates.

STATUS:Awaiting official documentation or verification criteria.
DEVELOPER WIRE

LiteLLM release pipeline compromise and poisoned PyPI package distribution (v1.107.0)

Supply-chain attack via hijacked GitHub CLI OAuth token deploying an infostealer and RAT on Python startup. Held on watchlist pending package ecosystem audit and token revocation disclosures.

STATUS:Awaiting official documentation or verification criteria.
DEVELOPER WIRE

Microsoft Windows Shell Mark of the Web bypass zero-day evolution (CVE-2026-96951)

Secondary monitoring of ongoing in-the-wild exploitation campaigns following initial monthly disclosure. Held on watchlist following initial disclosure.

STATUS:Awaiting official documentation or verification criteria.